NobleProg provides specialized AI Security training courses across Mississippi, catering to professionals and organizations seeking expert-led instruction. With a focus on accessible and high-quality education, we deliver comprehensive learning solutions tailored to the unique needs of learners in this region.
Guard artificial intelligence systems against emerging risks through practical, instructor-led instruction in AI Security.
These synchronous courses instruct participants on defending machine learning models, mitigating adversarial attacks, and establishing trustworthy, resilient AI frameworks for government applications.
Instruction is accessible via online live sessions using remote desktop or onsite live training in Mississippi, incorporating interactive exercises and real-world scenarios.
Onsite instruction may be provided at your facility in Mississippi or at a NobleProg corporate training center in Mississippi.
Also referred to as Secure AI, ML Security, or Adversarial Machine Learning.
NobleProg – Your Local Training Provider
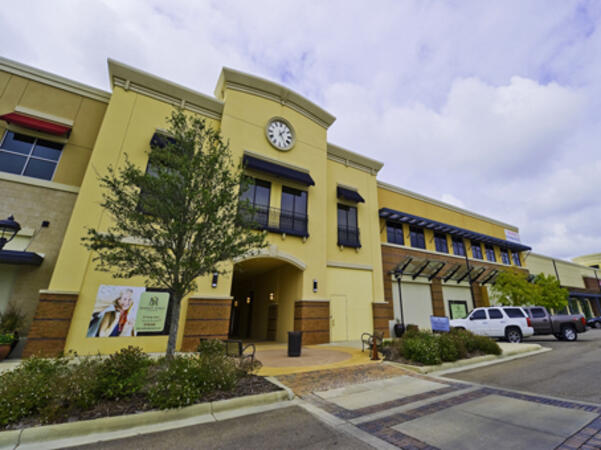
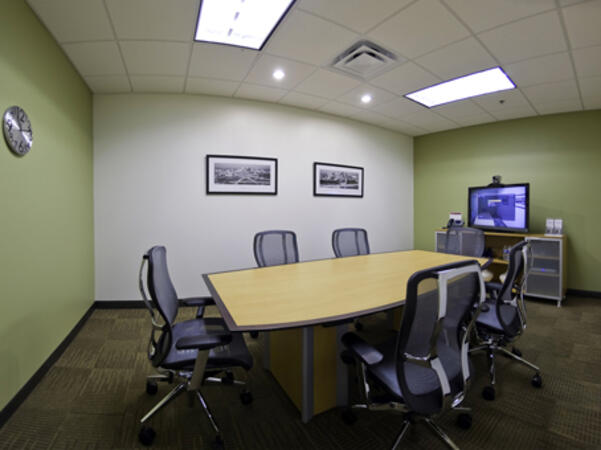
Flowood, MS – Regus at Market Street
232 Market Street, Flowood, United States, 39232
The venue is centrally located at Market Street Flowood, just off US‑25/Lakeland Drive and Old Fannin Road, with plentiful free on-site and nearby municipal parking. From Jackson‑Medgar Wiley Evers International Airport (JAN), about 10 miles northwest, a taxi or rideshare takes around 15 minutes via I‑55 North and Lakeland Drive. Public transit is available via JATRAN buses serving Lakeland Drive with stops just steps from the entrance, making it accessible even without a car. The pedestrian-friendly plaza also includes shaded seating and walking paths connecting retail and dining options.
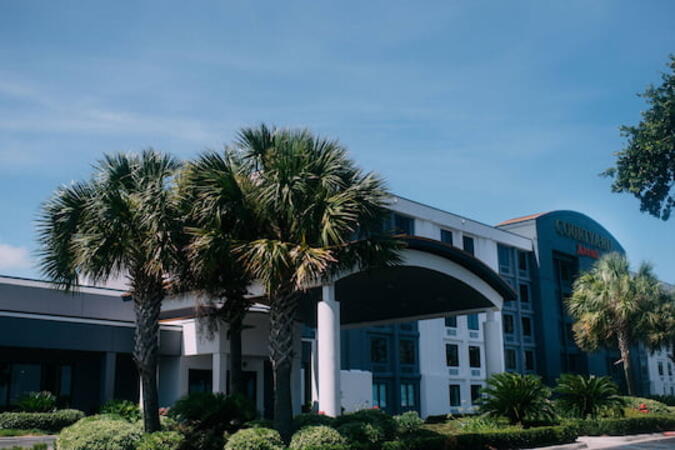
Gulfport, MS
1600 E Beach Blvd, Gulfport, United States, 39501
The venue is conveniently accessible by car via US‑90/Beach Boulevard, with on-site parking available for a daily fee. For those arriving by air, Gulfport–Biloxi International Airport (GPT) is just a short 5-minute drive away, approximately 5 miles via East Beach Boulevard. Public transportation is also an option, with Coast Transit Authority routes serving the area and the Gulfport Amtrak Station located about 0.7 miles from the venue. Rideshare services and local shuttles provide additional convenient transportation options.
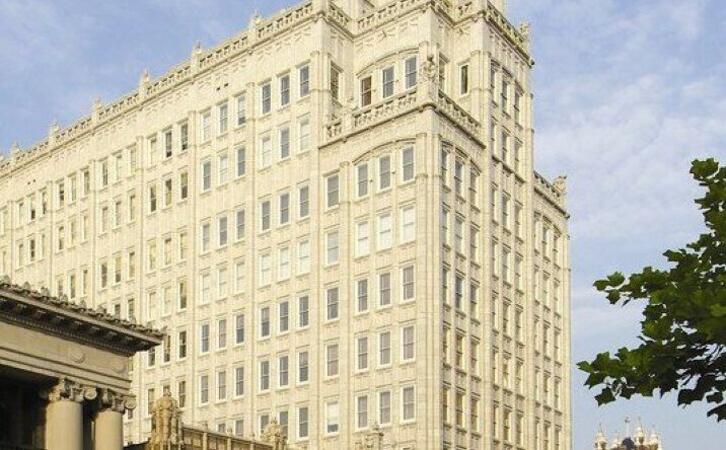
Jackson, MS - Regus at East Capitol Street
317 East Capitol Street, Jackson, United States, 39201
The venue is conveniently accessible by car via I‑55 and I‑20, with public parking options available near the Capitol area. For those using public transportation, several Capital Area Transit System (CATS) bus lines stop along East Capitol Street, providing easy access to the venue. Travelers arriving at Jackson–Medgar Wiley Evers International Airport (JAN) can reach the location in approximately 15 minutes by car, taking I‑55 North and East Capitol Street for a quick 10-mile drive.
This advanced ISACA course in Mississippi prepares professionals to oversee and secure AI systems for government. It addresses risk assessment, secure system design, and regulatory compliance, enabling leaders to align AI security with institutional objectives and significantly enhance operational resilience.
This instructor-led professional development session in Mississippi (online or in-person) is designed for junior to mid-level IT specialists seeking to integrate AI TRiSM principles into their institutional operations.
Upon completion of this training, participants will be equipped to:
Comprehend the fundamental concepts and strategic value of AI trust, risk, and security management.
Recognize and effectively reduce risks inherent in AI deployments.
Apply security best practices specifically tailored for AI environments.
Demonstrate knowledge of regulatory compliance and ethical imperatives in AI.
Formulate robust strategies for AI governance and operational oversight.
This instructor-led training in Mississippi covers governance, identity management, and red-teaming for agentic AI systems. Advanced practitioners will design secure deployments for government, implement least-privilege access, and execute adversarial testing to mitigate real-world threats in production environments.
This instructor-led live training in Mississippi (available online or onsite) targets intermediate-level AI and cybersecurity professionals seeking to mitigate security vulnerabilities specific to AI models and systems, with a focus on highly regulated sectors such as finance, data governance, and consulting for government applications.
Upon completion of this training, participants will be equipped to:
Identify adversarial attack vectors targeting AI systems and apply defensive strategies.
Apply model hardening techniques to safeguard machine learning pipelines.
Maintain data security and integrity within machine learning models.
Navigate regulatory compliance obligations associated with AI security for government and other public entities.
This instructor-led live training in Mississippi (online or onsite) is directed at senior security experts and machine learning specialists who aim to emulate threats against AI systems, detect vulnerabilities, and strengthen the resilience of operational AI models.
Upon completion, participants will possess the ability to:
TinyML is an approach to deploying machine learning models on low-power, resource-constrained devices operating at the network edge.
This instructor-led, live training (online or onsite) is aimed at advanced-level professionals who wish to secure TinyML pipelines and implement privacy-preserving techniques in edge AI applications.
At the conclusion of this course, participants will be able to:
Identify security risks unique to on-device TinyML inference.
Implement privacy-preserving mechanisms for edge AI deployments.
Harden TinyML models and embedded systems against adversarial threats.
Apply best practices for secure data handling in constrained environments.
Format of the Course
Engaging lectures supported by expert-led discussions.
This instructor-led, live training session, offered either online or onsite at Mississippi, is designed for mid-level engineering and security professionals. The program focuses on securing AI models deployed in edge environments against threats including device tampering, data leakage, adversarial inputs, and physical attacks.
Upon completion, participants will be equipped to:
Identify and evaluate security vulnerabilities in edge AI implementations.
Apply tamper-resistant mechanisms and encrypted inference methodologies.
Strengthen the resilience of edge-deployed models and secure data processing pipelines.
Execute threat mitigation strategies tailored for embedded and resource-constrained systems.
This instructor-led, live training in Mississippi (online or onsite) is designed for advanced-level professionals seeking to implement and evaluate methodologies such as federated learning, secure multiparty computation, homomorphic encryption, and differential privacy within production machine learning pipelines.
Upon completion of this training, participants will be equipped to:
Analyze and contrast critical privacy-preserving techniques in machine learning.
Develop federated learning systems utilizing open-source frameworks.
Implement differential privacy protocols for secure data sharing and model training.
Leverage encryption and secure computation methods to safeguard model inputs and outputs.
The integration of Artificial Intelligence (AI) into public sector operations introduces distinct challenges regarding operational risk, governance integrity, and cybersecurity resilience for federal, state, and local agencies.
This live, instructor-led training session, available both online and onsite, is designed specifically for government IT and risk management professionals. It targets those with limited prior exposure to AI, providing the necessary skills to evaluate, monitor, and secure AI systems within the regulatory and accountability frameworks of the public sector.
Upon completion, participants will be equipped to:
Interpret core risk concepts associated with AI systems, including bias, unpredictability, and model drift.
Apply AI-specific governance and auditing standards, such as the NIST AI RMF and ISO/IEC 42001, to government contexts.
Identify cybersecurity threats that target AI models and associated data pipelines.
Develop cross-departmental risk management strategies and ensure policy alignment for the responsible deployment of AI.
Course Format
Interactive instruction and discussion focused on public sector use cases relevant to government.
Practical exercises in applying AI governance frameworks and mapping policies.
Scenario-based threat modeling and risk evaluation activities.
Customization Options
Interested parties may contact us to discuss options for tailoring this training to specific agency needs.
This instructor-led, live training in Mississippi (available online or in-person) targets intermediate-level leaders responsible for overseeing AI systems in government and enterprise environments. The course focuses on responsible governance and security, ensuring alignment with emerging global frameworks such as the EU AI Act, GDPR, ISO/IEC 42001, and the U.S. Executive Order on AI.
By the conclusion of this training, participants will be equipped to:
Evaluate the legal, ethical, and regulatory implications of AI adoption across organizational units.
Apply major AI governance frameworks, including the EU AI Act, NIST AI Risk Management Framework, and ISO/IEC 42001.
Establish comprehensive security, auditing, and oversight policies for AI deployments in government and enterprise contexts.
Develop rigorous procurement and usage standards for both third-party and in-house AI systems.
This instructor-led, live training session in Mississippi (available online or onsite) is tailored for intermediate to advanced AI developers, architects, and product managers. The objective is to identify and mitigate risks associated with LLM-powered applications, including prompt injection, data leakage, and unfiltered output, while incorporating security controls like input validation, human-in-the-loop oversight, and output guardrails.
Upon completion of this training, participants will be able to:
Comprehend the core vulnerabilities of LLM-based systems
Apply secure design principles to LLM application architecture
Leverage tools such as Guardrails AI and LangChain for validation, filtering, and safety measures
Integrate techniques such as sandboxing, red teaming, and human-in-the-loop review into production-grade pipelines
This instructor-led, live training in Mississippi (online or onsite) targets intermediate-level professionals in machine learning and cybersecurity. It is designed to assist these individuals in understanding and mitigating emerging threats against AI models for government, employing both conceptual frameworks and hands-on defenses such as robust training and differential privacy.
Upon completion, participants will possess the capability to:
Identify and categorize AI-specific threats, including adversarial attacks, inversion, and poisoning.
Utilize the Adversarial Robustness Toolbox (ART) to simulate attacks and validate model integrity.
Implement practical defenses, such as adversarial training, noise injection, and privacy-preserving methods.
Develop threat-aware evaluation strategies for models in production environments.
This instructor-led, live training in Mississippi (online or onsite) is designed for entry-level IT security, risk, and compliance professionals seeking to master foundational AI security concepts, threat vectors, and global frameworks such as the NIST AI RMF and ISO/IEC 42001.
Upon completion of this training, participants will be equipped to:
Comprehend the distinct security risks inherent in AI systems.
Recognize specific threat vectors, including adversarial attacks, data poisoning, and model inversion.
Implement foundational governance models such as the NIST AI Risk Management Framework.
Align AI adoption with emerging standards, compliance guidelines, and ethical principles relevant to public sector operations.
Aligned with the latest OWASP GenAI Security Project guidance, participants will learn to identify, assess, and mitigate AI-specific threats through hands-on exercises and real-world scenarios.
This course offers a practical framework for securing modern AI-powered applications, APIs, copilots, and autonomous agents. Participants examine the distinctions between AI security and traditional web security, explore specific threats such as prompt injection, RAG poisoning, and agent abuse, and learn to protect AI systems through layered defenses including WAFs, AI gateways, API security, and guardrails. Through hands-on labs and real-world scenarios, participants develop the skills to identify AI attack patterns, secure LLM-based applications, and deploy effective runtime defenses suitable for production and government environments.
This course instructs software developers on the secure, design-level construction of AI-powered applications. Participants learn to protect chatbots, copilots, RAG pipelines, and AI agents against AI-specific threats, including prompt injection, data poisoning, tool misuse, secret leakage, and insecure model output. The curriculum covers secure prompt design, RAG security, least-privilege access control, guardrail implementation, and red-team testing, enabling developers to build AI features that are secure, reliable, and resilient in production environments.
This live, instructor-led training session in Mississippi (available online or onsite) is tailored for security engineers and compliance officers aiming to strengthen deployment security, manage model access, and oversee on-premise AI workloads for government operations.
This instructor-led, live training in Mississippi (online or onsite) is designed for security and ML engineers who must identify, test for, and defend against attacks on ML models and LLM-powered applications.
Read more...
Last Updated:
Testimonials (3)
inventory and identifying the different risk exposures within AI
Gary Cook - Cybersecurity and Information Technology Risk Division
Course - Introduction to AI Trust, Risk, and Security Management (AI TRiSM)
I really enjoyed learning about AI attacks and the tools out there to begin practicing and actively using for security testing. I took a lot of knowledge away which I didn't have at the beginning and the course met what I hoped it would be. My favorite part shown from the training was Comet Browser and was amazed at what it could do. Definitely something will be looking into more. Overall it was a great course and enjoyed learning all OWASP GenAI Top 10.
Patrick Collins - Optum
Course - OWASP GenAI Security
The profesional knolage and the way how he presented it before us
Online Secure AI training in Mississippi, AI Security training courses in Mississippi, Weekend Secure AI courses in Mississippi, Evening AI Security training in Mississippi, Secure AI instructor-led in Mississippi, Secure AI instructor-led in Mississippi, AI Security one on one training in Mississippi, Evening AI Security courses in Mississippi, Secure AI instructor in Mississippi, AI Security on-site in Mississippi, Secure AI coaching in Mississippi, Weekend Secure AI training in Mississippi, Online AI Security training in Mississippi, Secure AI classes in Mississippi, AI Security boot camp in Mississippi, Secure AI trainer in Mississippi, AI Security private courses in Mississippi